Security engineers building for the AI era
After years deploying and securing AI systems for large companies, we saw the same attacks keep succeeding because runtime protection was absent. We built one.
Why Repellox began
AI agents differ from traditional software: they accept natural language, send it to powerful tools, and act in the world. This creates an attack surface existing security tools were not built to cover: an adversary needs no code execution, only the right words.
Prompt injection is not a bug in one model or framework. It is a structural property of systems mixing trusted instructions and untrusted data, an architecture ubiquitous wherever AI is usefully deployed. Fine-tuning and system prompt guards help, but cannot solve runtime attacks from adversarial content arriving through external sources the model retrieves itself.
We founded Repellox in 2023 after years in infrastructure security and AI deployment engineering. Our aim: make runtime protection for AI agents as standard as TLS for web traffic: set it up once, let it work transparently, and never think about it again.
The team
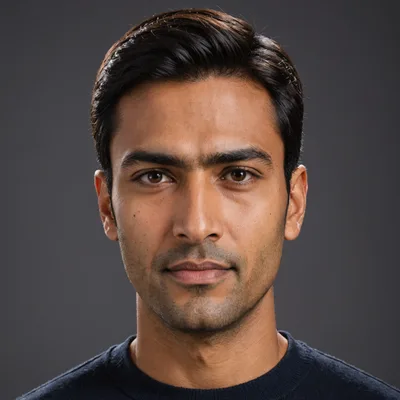
Trained in infrastructure security and AI deployment engineering, with years building and auditing production LLM pipelines in high-stakes environments before deciding the security tooling gap was the right full-time problem.
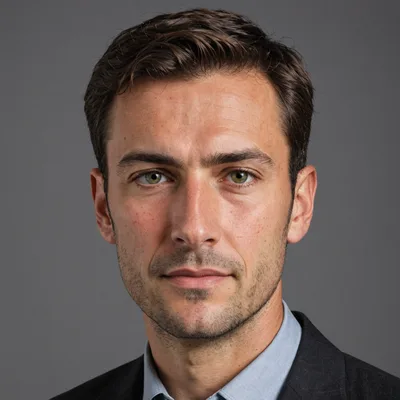
An ML systems engineer from low-latency inference infrastructure, he built Repellox's core inspection architecture, keeping it under 2ms p99. He focuses on making security a zero-cost abstraction for developers.
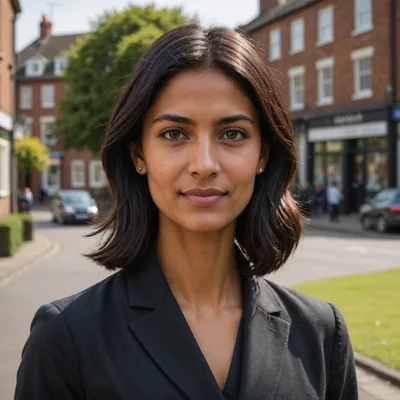
Red team researcher focused on adversarial ML, indirect injection, context poisoning, and multi-step agent attacks. She leads the threat intelligence program keeping Repellox detection signatures current as attack techniques emerge.
Funding
Repellox closed a $1.5M angel round in June 2025, backed by investors with backgrounds in security infrastructure and AI deployment. Headquartered in Boston, Massachusetts, we run a remote first engineering team.
We are not pursuing growth for its own sake. We are building long-lived infrastructure, and our funding lets us do so carefully.
Work with us or say hello
Have product questions, partnership requests, or want to discuss your security architecture? We read every email.